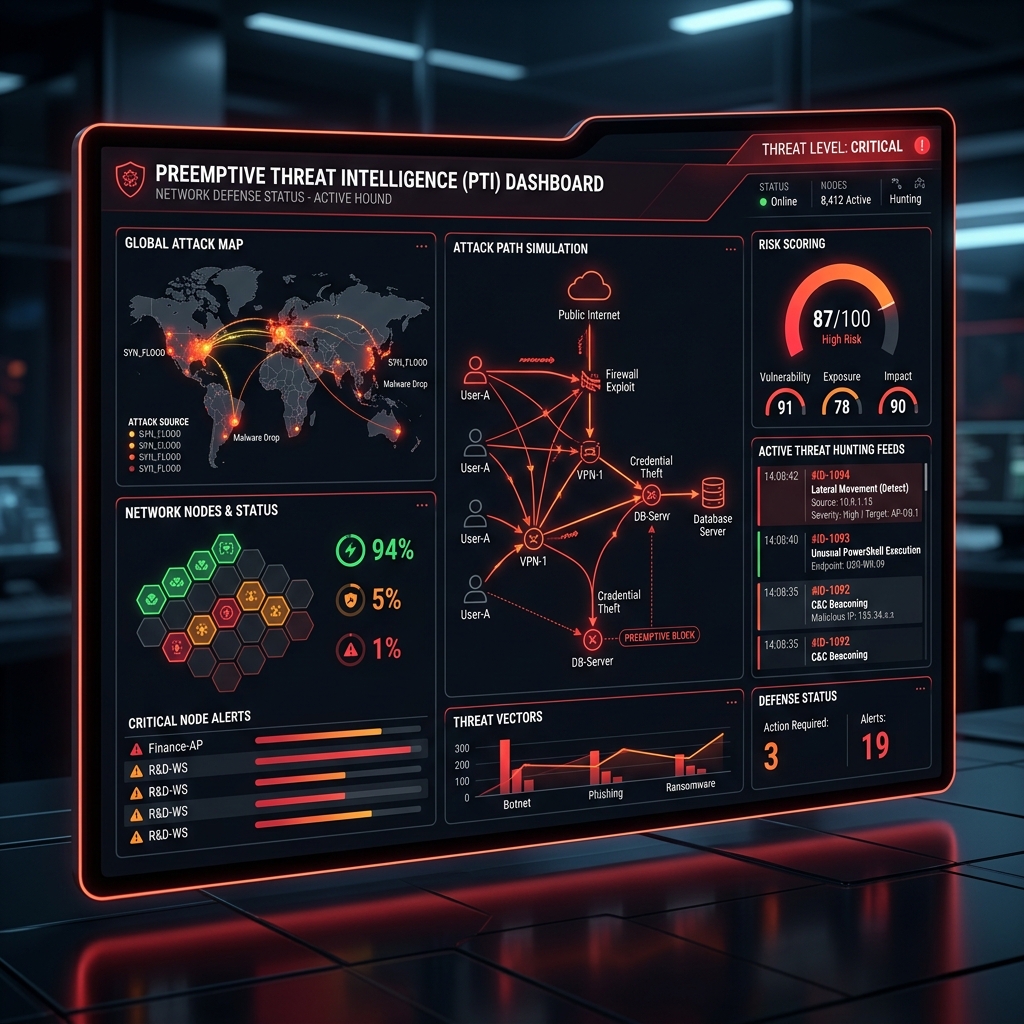
Preemptive Cybersecurity: 7 Actionable Strategies for Enterprise Threat Hunting in 2026

In the high-stakes landscape of digital operations, reactive defense is a losing strategy. Relying on alerts from legacy antivirus programs or firewall logs means your security operations center (SOC) only responds after a perimeter breach has already occurred. In 2026, forward-thinking organizations are shifting toward a Preemptive Cybersecurity posture. By proactively hunting for threats, identifying vulnerabilities, and neutralizing attackers before they execute payloads, security teams can prevent data breaches entirely.
Applying a Preemptive Cybersecurity framework requires combining advanced threat intelligence, automated attack simulation, and continuous exposure management. In this enterprise guide, we break down the 7 actionable strategies for threat hunting and proactive hardening to defend your infrastructure against modern cyber adversaries.
Table of Contents
- Why Preemptive Cybersecurity is the Essential Enterprise Shift
- The Threat Hunting Mindset: Assume Breach
- 7 Preemptive Cybersecurity Threat Hunting Strategies
- 1. Continuous Threat Exposure Management (CTEM)
- 2. Mapping Logs to the MITRE ATT&CK Framework
- 3. Deploying Deception Technologies (Honeypots)
- 4. Automating Breach and Attack Simulations (BAS)
- Implementing Preemptive Cybersecurity Detection Engines
- 6. Leveraging High-Fidelity Threat Intelligence Feeds
- 7. Securing Machine Identity and Access Paths
- Conclusion: The Proactive Cyber Defense Posture
Why Preemptive Cybersecurity is the Essential Enterprise Shift
The core philosophy of Preemptive Cybersecurity is to disrupt the adversary’s kill chain as early as possible. Historically, security teams focused heavily on mitigation: block the IP, quarantine the files, or clean the server. However, modern threat actors deploy AI-driven scanning tools and custom polymorphic malware that can bypass standard signature-based detection in seconds. Proactive defense seeks to make the enterprise infrastructure a hostile environment for attackers by removing access vectors before they are ever targeted.
This proactive stance targets all layers of the IT stack—from network nodes to cloud clusters. For platform engineers running distributed microservices, preemptive security requires locking down configurations. Review our architectural blueprint on Kubernetes Zero Trust Hardening to secure your orchestration environments and prevent lateral movement.
The Threat Hunting Mindset: Assume Breach
Threat hunting is the core operational component of a preemptive posture. Rather than waiting for an Endpoint Detection and Response (EDR) alert, threat hunters operate under the assumption that attackers are already inside the network. Hunters search for Indicators of Compromise (IOCs) and Indicators of Behavior (IOBs) that bypass automated filters. This process involves analyzing system logs, memory dumps, and network traffic flows to identify subtle anomalies.
For instance, an attacker might establish persistence by injecting a malicious script inside a containerized build pipeline. Ensuring container supply chain security is a foundational requirement. We recommend reading our guide on Docker Container Hardening to verify that runtime workloads run without root access, preventing hackers from escaping containers to the host system.
7 Preemptive Cybersecurity Threat Hunting Strategies
To successfully integrate threat hunting into your operations, implement the following 7 strategies across your security workflows.
1. Continuous Threat Exposure Management (CTEM)
CTEM is a structured framework that goes beyond simple vulnerability scanning. It requires continuously identifying, evaluating, and prioritizing risk across your digital assets. Focus on discovering shadow IT, misconfigured cloud buckets, and orphaned domains that attackers use as initial footholds.
2. Mapping Logs to the MITRE ATT&CK Framework
Standardize log aggregation around the MITRE ATT&CK matrix. By mapping your endpoint, cloud, and network logs to specific adversary tactics (like credential access or lateral movement), threat hunters can identify missing visibility areas and write targeted detection queries.
3. Deploying Deception Technologies (Honeypots)
Deception technology involves placing fake assets (like dummy databases, decoy file shares, or fake administrator credentials) within your network. Because legitimate users have no reason to access these resources, any interaction with a honeypot triggers an immediate, high-fidelity alert of internal reconnaissance.
4. Automating Breach and Attack Simulations (BAS)
Regular penetration testing is a periodic check; BAS provides continuous validation. By running automated, non-disruptive attack vectors against your production defenses, security teams can test whether firewalls, SIEMs, and EDR agents are detecting and blocking real-world adversary behavior.
Implementing Preemptive Cybersecurity Detection Engines
As systems integrate with generative artificial intelligence, security boundaries expand. Autonomous LLM agents are particularly prone to manipulation. Platform teams must build safety checks directly into AI inputs and outputs. Review our best practices on LLM Guardrails implementation to secure machine learning interfaces against prompt injection attacks.
6. Leveraging High-Fidelity Threat Intelligence Feeds
Integrate open-source and commercial threat intelligence feeds into your SIEM. By utilizing real-time data about active campaigns, command-and-control (C2) IP addresses, and file hashes, threat hunters can run retrospective queries to verify if internal nodes have contacted malicious endpoints.
7. Securing Machine Identity and Access Paths
Adversaries increasingly target service accounts, API keys, and machine identities to bypass perimeters. Managing these credentials securely is critical to preventing credential theft. We recommend reviewing the Non-Human Identity (NHI) Blueprint to secure machine-to-machine integrations and restrict service boundaries.
Let’s review the difference between reactive and preemptive operations:
| Metric | Reactive Security (SOC 1.0) | Preemptive Cybersecurity (SOC 2.0) |
|---|---|---|
| Trigger | Security alert (EDR, Firewall, SIEM) | Hypothesis-driven search, threat intelligence |
| Approach | Mitigate known threats and recover systems | Harden systems, hunt active threats, deploy decoys |
| Data Source | Post-incident logs and telemetry | Continuous asset visibility, attack paths |
| Primary KPI | Mean Time to Resolve (MTTR) | Reduction of attack surface and exposure window |
Conclusion: The Proactive Cyber Defense Posture
Building a resilient enterprise requires moving beyond passive defense. By adopting a Preemptive Cybersecurity model—combining exposure management, threat hunting, deception technology, and hardcoded security guardrails—organizations can shift the balance of power back to the defenders, keeping their infrastructure safe from advanced threats in 2026.
For additional details on threat hunting techniques, explore the official guidelines on the CISA Resources Portal and the database of tactics on the MITRE ATT&CK Matrix.